Cybersecurity Talent Gap: 3 Urgent Roles U.S. Companies Need to Fill by Late 2026, Offering 20%+ Salary Premiums
The digital landscape is expanding at an unprecedented pace, bringing with it both immense opportunities and formidable threats. As businesses increasingly rely on interconnected systems and cloud-based solutions, the importance of robust cybersecurity measures has never been higher. However, a critical challenge looms large over U.S. companies: a widening cybersecurity talent gap. This isn’t just a shortage; it’s an urgent crisis demanding immediate attention, with significant implications for national security, economic stability, and individual privacy. By late 2026, the demand for skilled cybersecurity professionals is projected to skyrocket, leading to substantial salary premiums for those in critical roles, often exceeding 20%.
The cybersecurity talent gap is a multifaceted problem, driven by the rapid evolution of cyber threats, the increasing complexity of IT infrastructures, and a persistent lack of qualified individuals entering the field. This article will delve into the current state of the cybersecurity talent gap, identify three urgent roles U.S. companies desperately need to fill, and explore strategies to attract and retain these highly sought-after professionals.
The Alarming State of the Cybersecurity Talent Gap
Reports from leading industry organizations, such as (ISC)² and CyberSeek, consistently highlight the severe shortage of cybersecurity professionals globally and, particularly, in the United States. The 2023 (ISC)² Cybersecurity Workforce Study revealed a global cybersecurity workforce gap of 4 million people, with the U.S. alone needing hundreds of thousands more professionals to adequately defend its digital infrastructure. This gap is not merely a numbers game; it’s about a deficit of specialized skills required to combat sophisticated and evolving cyber threats.
The consequences of this cybersecurity talent gap are dire. Understaffed security teams are often overwhelmed, leading to increased vulnerability to attacks, slower response times to breaches, and ultimately, greater financial and reputational damage for organizations. The average cost of a data breach continues to climb, and a significant contributing factor is often the lack of skilled personnel to prevent, detect, and respond effectively.
Several factors contribute to this persistent shortage:
- Rapidly Evolving Threat Landscape: Cybercriminals are constantly innovating, developing new attack vectors and sophisticated malware. Security professionals need to stay ahead of these threats, requiring continuous learning and adaptation.
- Complexity of Modern IT Environments: The shift to cloud computing, IoT devices, and remote work has expanded the attack surface, making cybersecurity more complex than ever.
- Lack of Qualified Entrants: There aren’t enough graduates with the necessary skills entering the workforce. Traditional education pathways often struggle to keep pace with industry demands.
- High Burnout Rate: The demanding nature of cybersecurity work, coupled with long hours and constant pressure, can lead to burnout, further exacerbating attrition rates.
- Perception and Awareness: Many individuals are unaware of the diverse and rewarding career opportunities within cybersecurity, or they perceive the field as overly technical and inaccessible.
Addressing the cybersecurity talent gap is not just a recruitment challenge; it’s a strategic imperative for businesses and governments alike. Failure to do so will leave organizations exposed to an increasingly hostile digital environment.
Three Urgent Roles Offering Significant Salary Premiums by Late 2026
While the entire cybersecurity sector is experiencing a talent crunch, some roles are particularly critical due to their direct impact on an organization’s security posture and the specialized skills they require. U.S. companies are actively seeking to fill these positions, and by late 2026, professionals with the right expertise can expect to command salary premiums of 20% or more above current market rates.
1. Cloud Security Architect/Engineer
As organizations continue their rapid migration to cloud platforms (AWS, Azure, Google Cloud), the need for specialized cloud security expertise has exploded. A Cloud Security Architect or Engineer is responsible for designing, implementing, and managing security controls within cloud environments. This role is crucial because traditional on-premise security models do not directly translate to the cloud, which introduces new vulnerabilities and compliance challenges.
Why this role is urgent: Misconfigurations in cloud environments are a leading cause of data breaches. Without skilled cloud security professionals, companies risk exposing sensitive data, violating compliance regulations, and suffering significant financial losses. The rapid adoption of multi-cloud strategies further complicates security, demanding experts who can navigate complex, hybrid environments.
Key responsibilities include:
- Designing and implementing secure cloud architectures.
- Ensuring compliance with industry standards (e.g., NIST, ISO 27001, HIPAA, GDPR) in cloud settings.
- Developing and enforcing cloud security policies and procedures.
- Configuring and managing cloud security tools (e.g., CASBs, CSPMs, CWPPs).
- Performing security assessments and penetration testing on cloud infrastructure.
- Automating security operations in CI/CD pipelines.
Required skills: Deep understanding of cloud platforms (AWS, Azure, GCP), cloud security best practices, identity and access management (IAM), network security in the cloud, container security (Kubernetes, Docker), DevSecOps principles, scripting (Python, PowerShell), and strong communication skills.
Expected Salary Premium (by late 2026): 20-30% above current averages, pushing salaries well into the six figures, especially for those with multiple cloud certifications and hands-on experience.
2. Incident Response Analyst/Manager
Even with the best preventative measures, breaches are almost inevitable. When an attack occurs, an Incident Response (IR) Analyst or Manager is the first line of defense, responsible for detecting, analyzing, containing, eradicating, and recovering from cyber incidents. Their ability to act swiftly and effectively can significantly mitigate the damage caused by a breach.
Why this role is urgent: The speed and sophistication of modern cyberattacks mean that every second counts during an incident. A well-trained IR team can reduce downtime, minimize data loss, and prevent reputational damage. The increasing regularity and severity of ransomware attacks and supply chain compromises have made robust incident response capabilities non-negotiable.
Key responsibilities include:
- Monitoring security alerts and investigating potential incidents.
- Analyzing malware, network traffic, and system logs to identify attack vectors.
- Containing and eradicating threats from affected systems.
- Coordinating with internal teams and external stakeholders during an incident.
- Developing and refining incident response plans and playbooks.
- Conducting post-incident analysis and recommending preventative measures.
Required skills: Strong analytical and problem-solving abilities, knowledge of threat intelligence, digital forensics, reverse engineering, SIEM tools, endpoint detection and response (EDR), network protocols, scripting, and excellent communication under pressure.
Expected Salary Premium (by late 2026): 25-35% above current averages, reflecting the immense pressure and critical nature of the role. Experienced IR professionals with certifications like GCIH or GCFA will be in extremely high demand.
3. Application Security Engineer (AppSec)
As software development cycles accelerate and applications become the primary interface for customer interaction, securing these applications from design to deployment is paramount. An Application Security Engineer focuses on identifying, fixing, and preventing vulnerabilities in software applications throughout the entire software development lifecycle (SDLC).
Why this role is urgent: Web applications and APIs are frequent targets for attackers, often serving as gateways into an organization’s internal network. With the rise of DevOps and continuous integration/continuous delivery (CI/CD), security needs to be integrated from the very beginning, shifting left in the development process. A single vulnerability in a critical application can expose millions of users and vast amounts of data.
Key responsibilities include:
- Conducting security code reviews and vulnerability assessments.
- Performing penetration testing and static/dynamic application security testing (SAST/DAST).
- Advising development teams on secure coding practices and security best practices.
- Integrating security tools and processes into CI/CD pipelines (DevSecOps).
- Developing security requirements and threat models for new applications.
- Responding to security incidents related to applications.
Required skills: Proficiency in various programming languages (e.g., Python, Java, C#, JavaScript), deep understanding of common application vulnerabilities (OWASP Top 10), experience with security testing tools, knowledge of secure SDLC, API security, container security, and strong collaboration skills.
Expected Salary Premium (by late 2026): 20-30% above current averages, driven by the increasing complexity of applications and the critical need to embed security from the ground up.
Strategies for U.S. Companies to Bridge the Cybersecurity Talent Gap
Filling these urgent roles and addressing the broader cybersecurity talent gap requires a multi-pronged approach from U.S. companies. It’s not enough to simply offer higher salaries; organizations must rethink their recruitment, retention, and development strategies.
1. Invest in Training and Upskilling Current Employees
One of the most effective ways to combat the cybersecurity talent gap is to cultivate talent internally. Many IT professionals already possess foundational knowledge that can be leveraged for cybersecurity roles. Companies should establish robust training programs, offer certifications, and provide clear career pathways for employees interested in transitioning into cybersecurity.
- Cybersecurity Academies: Create internal academies or partner with educational institutions to offer specialized cybersecurity training.
- Certification Programs: Sponsor employees to obtain industry-recognized certifications (e.g., CompTIA Security+, CEH, CISSP, GIAC).
- Mentorship Programs: Pair experienced cybersecurity professionals with junior staff to facilitate knowledge transfer and skill development.
2. Broaden Recruitment Strategies and Focus on Diversity
Companies often limit their search to candidates with traditional cybersecurity backgrounds, overlooking a wealth of potential talent. Expanding recruitment efforts to include individuals from diverse educational backgrounds, including those with non-traditional degrees, liberal arts, or even unrelated fields, can yield unexpected talent. Diversity in thought and experience can also lead to more innovative security solutions.
- Apprenticeships and Internships: Establish programs to bring in entry-level talent and provide them with on-the-job training.
- Focus on Soft Skills: While technical skills are vital, emphasize critical thinking, problem-solving, communication, and adaptability, which can be taught and developed.
- Reach Out to Underrepresented Groups: Actively recruit women, minorities, and veterans, who often possess valuable skills and perspectives.
3. Foster a Culture of Continuous Learning and Development
The cybersecurity landscape is constantly changing, meaning that skills acquired today may be obsolete tomorrow. Companies must create an environment that encourages and supports continuous learning. This not only keeps the workforce current but also serves as a powerful retention tool.
- Dedicated Training Budgets: Allocate funds specifically for cybersecurity training, conferences, and online courses.
- Time for Learning: Allow employees dedicated time during work hours for professional development.
- Internal Knowledge Sharing: Encourage team members to share insights, best practices, and lessons learned from incidents.
4. Optimize Compensation and Benefits Packages
While not the only factor, competitive compensation is crucial, especially for high-demand roles. Companies need to be prepared to offer significant salary premiums for the urgent roles identified earlier. However, compensation goes beyond just salary.
- Performance Bonuses: Reward cybersecurity teams for successful incident prevention, rapid response, and innovative solutions.
- Comprehensive Benefits: Offer attractive health, retirement, and wellness programs.
- Work-Life Balance: Given the high-pressure nature of cybersecurity, offering flexible work arrangements, remote work options, and ample paid time off can be a significant draw.
5. Embrace Automation and AI in Security Operations
Automation and Artificial Intelligence (AI) can help alleviate some of the workload on understaffed security teams by handling repetitive tasks, analyzing vast amounts of data, and accelerating threat detection and response. This allows human experts to focus on more complex, strategic challenges.
- Automated Threat Detection: Implement AI-powered tools for anomaly detection and behavioral analysis.
- Security Orchestration, Automation, and Response (SOAR): Utilize SOAR platforms to automate incident response playbooks and streamline workflows.
- AI for Vulnerability Management: Employ AI to prioritize vulnerabilities and suggest remediation steps.
By integrating these technologies, companies can make their existing cybersecurity teams more efficient and effective, reducing the pressure to fill every single open position immediately with a human.
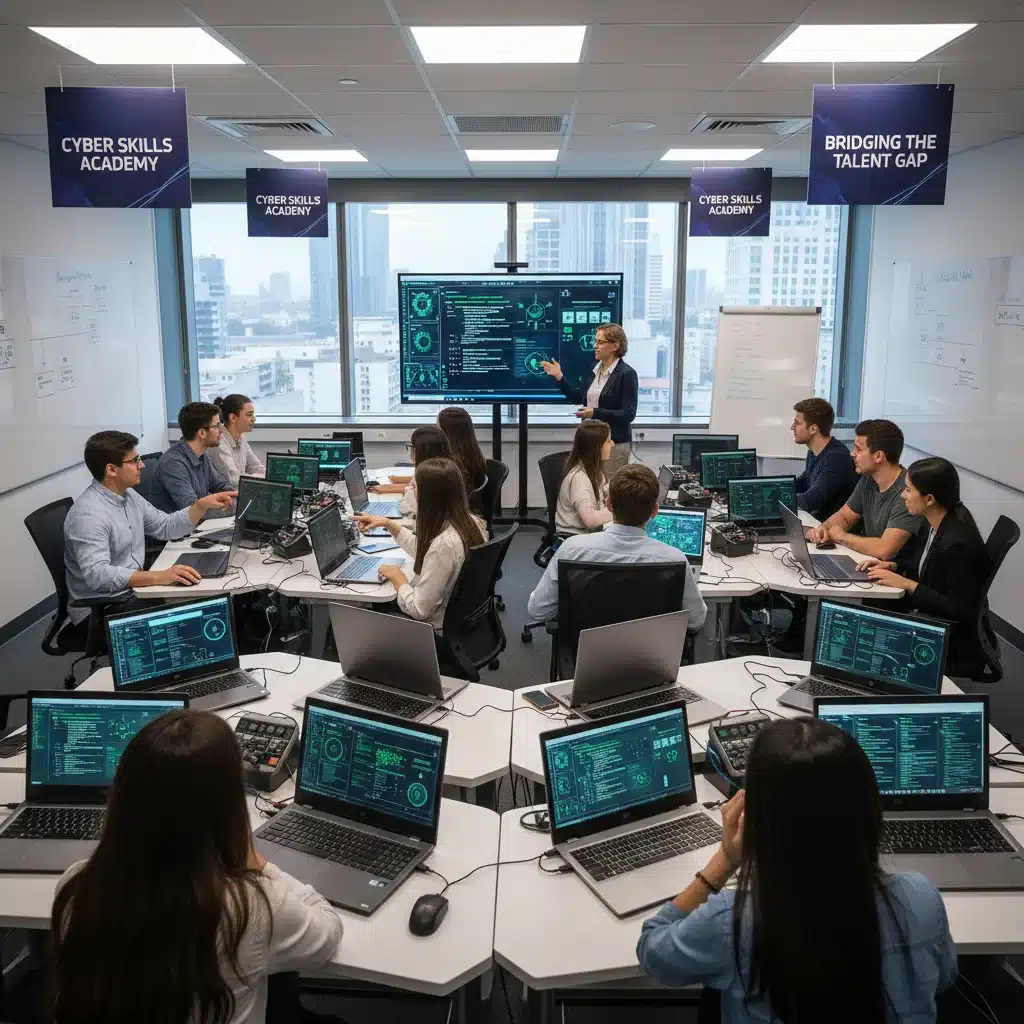
6. Partner with Educational Institutions and Government Programs
To address the long-term cybersecurity talent gap, collaboration between industry, academia, and government is essential. Companies can play a vital role in shaping future curricula and supporting educational initiatives.
- Curriculum Development: Provide input to universities and colleges on the skills and technologies most needed in the industry.
- Guest Lecturers and Workshops: Send cybersecurity professionals to speak at schools and conduct workshops to inspire students.
- Sponsorships and Scholarships: Fund scholarships or programs for students pursuing cybersecurity degrees or certifications.
- Government Initiatives: Engage with government-sponsored cybersecurity workforce development programs.
The Future of Cybersecurity Careers
The cybersecurity talent gap, while challenging, also presents immense opportunities for individuals looking to enter a dynamic and impactful field. The demand for skilled professionals is not going to diminish; if anything, it will intensify. This ensures job security, competitive compensation, and a continuous learning environment for those who choose a career in cybersecurity.
For U.S. companies, proactively addressing the cybersecurity talent gap is no longer optional. It is a fundamental component of risk management and business continuity. By understanding the urgent need for roles like Cloud Security Architects, Incident Response Analysts, and Application Security Engineers, and by implementing comprehensive strategies for recruitment, training, and retention, organizations can build resilient security teams capable of defending against the ever-growing array of cyber threats.
The 20%+ salary premiums projected for these critical roles by late 2026 are a clear indicator of their value and the desperate need within the industry. Investing in cybersecurity talent is not an expense; it is an investment in the future security and success of the organization.
Conclusion
The cybersecurity talent gap is a pressing issue with far-reaching implications for U.S. companies. The urgent need to fill roles such as Cloud Security Architect, Incident Response Analyst, and Application Security Engineer is driving significant salary premiums, making these some of the most lucrative and impactful careers in technology. Organizations that recognize the severity of this gap and proactively implement robust strategies for attracting, developing, and retaining top cybersecurity talent will be better positioned to protect their assets, maintain customer trust, and thrive in an increasingly digital and threat-laden world. The time to act is now, to secure not just data, but the future.
Author