2026 National Cybersecurity Framework: 5 Steps to Compliance
The digital landscape is a dynamic battleground, constantly evolving with new threats and vulnerabilities. In this ever-changing environment, robust cybersecurity is not merely an option but a fundamental necessity for organizations of all sizes and sectors. As we look towards the future, the 2026 National Cybersecurity Framework emerges as a critical guide, offering a structured approach to managing and reducing cybersecurity risks. This framework, often seen as a benchmark for best practices, is designed to help organizations build resilience against sophisticated cyberattacks. Understanding and implementing its principles is paramount for ensuring the integrity, confidentiality, and availability of your digital assets.
Many organizations find the prospect of navigating new regulatory frameworks daunting. The sheer volume of information, coupled with the technical complexities involved, can make achieving compliance seem like an insurmountable task. However, breaking down the framework into manageable steps can demystify the process and provide a clear roadmap to success. This article aims to do just that, offering practical, actionable solutions to help your organization achieve and maintain cybersecurity framework compliance with the 2026 National Cybersecurity Framework.
We will delve into five essential steps that will guide you through the journey from initial assessment to continuous improvement. Each step is designed to build upon the last, creating a comprehensive and adaptive cybersecurity posture. By the end of this guide, you will have a clear understanding of what it takes to protect your organization effectively in the face of escalating cyber threats, ensuring you are well-prepared for the challenges of 2026 and beyond.
Understanding the 2026 National Cybersecurity Framework
Before we dive into the practical steps, it’s crucial to grasp the foundational aspects of the 2026 National Cybersecurity Framework. While specific details of the 2026 iteration might still be under development or refinement, it’s safe to assume it will build upon previous versions, such as the widely recognized NIST Cybersecurity Framework (CSF). The goal remains consistent: to provide a flexible, risk-based approach to cybersecurity that can be adopted by organizations across various sectors, regardless of their size or cybersecurity maturity level.
What is a National Cybersecurity Framework?
A national cybersecurity framework typically provides a common language and systematic methodology for managing cybersecurity risk. It is not a one-size-fits-all solution but rather a set of guidelines, best practices, and standards designed to improve an organization’s ability to prevent, detect, and respond to cyberattacks. These frameworks are often developed by government agencies, like the National Institute of Standards and Technology (NIST) in the United States, in collaboration with industry experts and stakeholders.
Key Components of Such Frameworks
While the 2026 framework will have its unique nuances, it will likely retain core components seen in established frameworks. These generally include:
- Core Functions: These are the high-level cybersecurity activities that an organization should undertake. Common functions include Identify, Protect, Detect, Respond, and Recover.
- Categories: Subdivisions of the core functions, providing more granular detail on specific activities.
- Subcategories: Specific outcomes of technical and management activities.
- Informative References: Specific sections of standards, guidelines, and practices that illustrate methods to achieve the outcomes associated with each subcategory.
The emphasis of these frameworks is often on risk management. Instead of prescribing specific technologies or solutions, they encourage organizations to understand their unique risk profile and implement controls that are proportionate to those risks. This approach allows for greater adaptability and ensures that cybersecurity investments are aligned with business objectives.
Why is 2026 Cybersecurity Framework Compliance Important?
Achieving cybersecurity framework compliance offers numerous benefits beyond simply avoiding penalties. It:
- Enhances Security Posture: Provides a structured way to identify vulnerabilities and implement robust controls.
- Improves Risk Management: Allows organizations to prioritize and manage cybersecurity risks effectively.
- Builds Trust: Demonstrates a commitment to protecting sensitive data, enhancing customer and partner confidence.
- Facilitates Communication: Offers a common language for discussing cybersecurity issues internally and externally.
- Supports Business Continuity: Reduces the likelihood and impact of cyber incidents, ensuring business operations can continue.
- Meets Regulatory Requirements: Helps organizations comply with various industry-specific regulations and legal mandates.
The 2026 framework will likely reflect the evolving threat landscape, incorporating lessons learned from recent cyber incidents and addressing emerging technologies like AI, IoT, and quantum computing. Therefore, proactive engagement with its principles will be crucial for any organization aiming to remain secure and competitive.
Step 1: Comprehensive Risk Assessment and Gap Analysis
The first and most critical step towards achieving cybersecurity framework compliance is to understand where you stand. This involves conducting a thorough risk assessment and a detailed gap analysis against the requirements of the 2026 National Cybersecurity Framework. You cannot protect what you don’t understand, and you cannot improve what you haven’t measured.
Conducting a Thorough Risk Assessment
A risk assessment identifies potential threats to your organization’s information systems and data, evaluates the likelihood of these threats occurring, and assesses their potential impact. This process involves:
- Asset Identification: Catalog all critical information assets, including hardware, software, data, intellectual property, and services. Understand their value to the organization.
- Threat Identification: Identify potential threats that could exploit vulnerabilities. These can be external (e.g., cybercriminals, nation-state actors, natural disasters) or internal (e.g., disgruntled employees, accidental errors).
- Vulnerability Identification: Discover weaknesses in your systems, processes, and people that could be exploited by threats. This includes technical vulnerabilities (e.g., unpatched software, misconfigured systems) and human vulnerabilities (e.g., lack of awareness, weak passwords).
- Likelihood and Impact Analysis: For each identified risk, assess the probability of it occurring and the potential business impact if it does. This helps in prioritizing risks.
- Risk Prioritization: Rank risks based on their severity (likelihood x impact) to focus resources on the most critical areas.
The output of your risk assessment should be a clear understanding of your organization’s risk profile, highlighting the most significant cyber threats you face.
Performing a Gap Analysis Against the 2026 Framework
Once you understand your risks, the next step is to measure your current cybersecurity capabilities against the specific controls and guidelines outlined in the 2026 National Cybersecurity Framework. This gap analysis will reveal where your current practices fall short of the framework’s requirements.
- Mapping Current Controls: Document all existing cybersecurity policies, procedures, technologies, and practices.
- Framework Cross-Referencing: Compare your current controls against each subcategory and requirement of the 2026 framework. For each requirement, determine if your organization fully meets it, partially meets it, or does not meet it at all.
- Identifying Gaps: Clearly identify the areas where your current state deviates from the desired state as defined by the framework. These are your gaps.
- Documenting Discrepancies: For each gap, document the specific framework requirement not met, the current state, and the desired state.
This detailed analysis will provide the foundation for developing a targeted action plan. Without a clear understanding of your gaps, efforts to achieve cybersecurity framework compliance will be unfocused and inefficient.
Step 2: Developing a Tailored Implementation Plan
With a comprehensive understanding of your risks and compliance gaps, the next step is to develop a strategic and actionable implementation plan. This plan should detail the specific actions required to address identified deficiencies and achieve full cybersecurity framework compliance.
Prioritizing Actions Based on Risk
Not all gaps are created equal. Your implementation plan must prioritize actions based on the criticality of the risks they mitigate and the ease of implementation. Focus on:
- High-Risk, High-Impact Gaps: Address these first. These are the vulnerabilities that, if exploited, could lead to significant financial loss, reputational damage, or operational disruption.
- Quick Wins: Identify actions that can be implemented relatively quickly and with minimal resources, providing immediate improvements to your security posture.
- Dependencies: Recognize that some actions may be prerequisites for others. Structure your plan to account for these dependencies.
A well-prioritized plan ensures that resources are allocated effectively, maximizing the impact of your cybersecurity investments.
Defining Specific Remediation Strategies
For each identified gap, outline a clear remediation strategy. This includes:
- Policy and Procedure Updates: Revising or creating new cybersecurity policies, standards, and operational procedures to align with the framework.
- Technology Implementation: Acquiring and deploying new security tools (e.g., SIEM, EDR, IAM, vulnerability scanners) or optimizing existing ones.
- Process Improvements: Enhancing incident response plans, data backup and recovery procedures, access control mechanisms, and patch management processes.
- Training and Awareness Programs: Developing and delivering training to employees on cybersecurity best practices, phishing awareness, and data handling protocols.
Each strategy should be detailed, specifying the actions to be taken, the responsible parties, the resources required, and the expected timeline for completion.
Establishing Roles, Responsibilities, and Timelines
A successful implementation plan requires clear accountability. Define:
- Roles and Responsibilities: Assign specific tasks and responsibilities to individuals or teams within your organization. This includes executive sponsorship, IT security teams, legal, HR, and other relevant departments.
- Timelines: Set realistic deadlines for the completion of each action item. Break down larger initiatives into smaller, more manageable milestones.
- Resource Allocation: Ensure that adequate budget, personnel, and technological resources are allocated to support the implementation efforts.
Regular communication and progress tracking are essential to keep the implementation on schedule and to address any roadblocks promptly. This structured approach is fundamental for effective cybersecurity framework compliance.
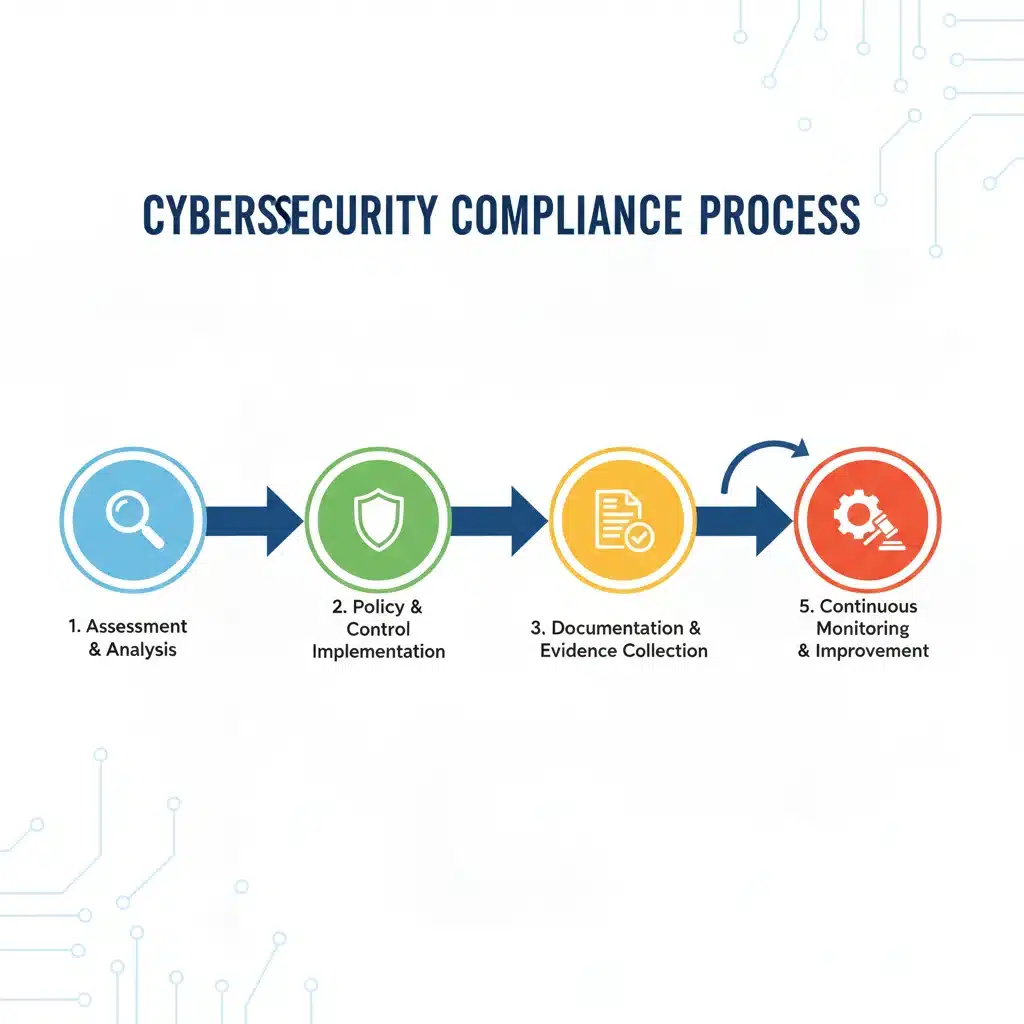
Step 3: Implementing Controls and Security Measures
With a robust implementation plan in hand, the next phase is the actual execution – putting the identified controls and security measures into practice. This is where the theoretical aspects of cybersecurity framework compliance translate into tangible improvements in your organization’s security posture.
Technical Implementations
This involves deploying and configuring various security technologies. Key areas include:
- Network Security: Implementing firewalls, intrusion detection/prevention systems (IDS/IPS), secure network segmentation, and robust Wi-Fi security protocols.
- Endpoint Security: Deploying advanced antivirus/anti-malware solutions, endpoint detection and response (EDR), and ensuring all devices are regularly patched and configured securely.
- Data Security: Implementing encryption for data at rest and in transit, data loss prevention (DLP) solutions, and secure data backup and recovery systems.
- Access Management: Establishing strong identity and access management (IAM) practices, including multi-factor authentication (MFA), role-based access control (RBAC), and regular access reviews.
- Vulnerability Management: Implementing regular vulnerability scanning and penetration testing programs to identify and remediate weaknesses proactively.
- Security Information and Event Management (SIEM): Deploying SIEM solutions to collect, analyze, and correlate security events from various sources, enabling faster detection of threats.
Each technical implementation should be thoroughly tested to ensure it functions as intended and integrates seamlessly with existing systems.
Policy and Process Integration
Technology alone is not enough; strong policies and well-defined processes are equally crucial. This step involves:
- Policy Enforcement: Ensuring that updated cybersecurity policies (e.g., acceptable use, data classification, incident response) are communicated, understood, and enforced across the organization.
- Procedure Development: Creating detailed operational procedures for tasks like secure configuration, patch management, incident handling, and third-party risk management.
- Change Management: Integrating security considerations into your organization’s change management processes to prevent new vulnerabilities from being introduced.
- Supply Chain Risk Management: Implementing processes to assess and manage the cybersecurity risks posed by third-party vendors and suppliers.
These policies and processes provide the governance structure necessary to maintain cybersecurity framework compliance over time.
Employee Training and Awareness
Humans are often considered the weakest link in the security chain, but with proper training, they can become your strongest defense. This step includes:
- Regular Security Awareness Training: Conducting mandatory training for all employees on topics such as phishing, social engineering, password hygiene, and safe internet usage.
- Role-Specific Training: Providing specialized training for employees with elevated access privileges or specific security responsibilities (e.g., IT staff, incident response teams).
- Phishing Simulations: Conducting simulated phishing attacks to test employee vigilance and reinforce training concepts.
- Culture of Security: Fostering a security-conscious culture where employees understand their role in protecting organizational assets and feel empowered to report suspicious activities.
Effective training transforms employees from potential vulnerabilities into active participants in maintaining cybersecurity framework compliance.
Step 4: Monitoring, Testing, and Continuous Improvement
Achieving cybersecurity framework compliance is not a one-time event; it’s an ongoing process. The digital threat landscape is constantly evolving, meaning your security posture must evolve with it. This step focuses on continuous monitoring, regular testing, and a commitment to perpetual improvement.
Establishing Continuous Monitoring Systems
Effective monitoring allows you to detect security incidents and deviations from your compliance baseline in real-time. This involves:
- Log Management and Analysis: Centralizing and analyzing logs from all critical systems, applications, and security devices to identify suspicious activities or anomalies.
- Intrusion Detection/Prevention Systems (IDS/IPS): Continuously monitoring network traffic for malicious activity and policy violations.
- Security Information and Event Management (SIEM): Utilizing SIEM solutions to correlate events, generate alerts, and provide a holistic view of your security environment.
- User and Entity Behavior Analytics (UEBA): Employing UEBA tools to detect unusual user or system behavior that might indicate a compromise.
- Threat Intelligence Integration: Incorporating up-to-date threat intelligence feeds to identify emerging threats and vulnerabilities relevant to your organization.
Continuous monitoring provides the visibility needed to respond swiftly to potential security breaches, a cornerstone of effective cybersecurity framework compliance.
Regular Security Testing and Audits
Periodic testing and audits are crucial to validate the effectiveness of your implemented controls and to uncover new vulnerabilities. Key activities include:
- Vulnerability Assessments: Regularly scanning your systems and applications for known vulnerabilities.
- Penetration Testing: Engaging ethical hackers to simulate real-world attacks against your systems to identify exploitable weaknesses.
- Internal and External Audits: Conducting regular internal audits to assess compliance with your policies and the 2026 framework, and engaging external auditors for independent verification.
- Security Control Reviews: Periodically reviewing the configuration and effectiveness of all security controls.
- Incident Response Drills: Conducting tabletop exercises and simulated incident response scenarios to test the readiness and effectiveness of your incident response plan.
These testing mechanisms provide objective evidence of your security posture and help identify areas requiring further attention for cybersecurity framework compliance.
Implementing a Continuous Improvement Cycle
The insights gained from monitoring and testing should feed directly into a continuous improvement cycle. This involves:
- Feedback Loop: Establishing mechanisms to collect feedback from security incidents, audit findings, vulnerability scans, and employee suggestions.
- Action Plan Refinement: Regularly updating your implementation plan based on new findings, emerging threats, and changes in the 2026 framework.
- Technology Updates: Staying abreast of new security technologies and upgrading existing ones as needed to maintain optimal protection.
- Policy and Procedure Revision: Adapting policies and procedures to reflect changes in the threat landscape, technological advancements, and organizational needs.
- Training Refreshers: Providing ongoing training and awareness campaigns to keep employees informed about the latest threats and best practices.
This iterative process ensures that your cybersecurity program remains agile, resilient, and aligned with the evolving requirements for cybersecurity framework compliance.
Step 5: Documentation, Reporting, and Stakeholder Communication
The final, but by no means least important, step in achieving and maintaining cybersecurity framework compliance involves thorough documentation, transparent reporting, and effective communication with all relevant stakeholders. This ensures accountability, provides evidence of compliance, and fosters a shared understanding of cybersecurity within the organization.
Comprehensive Documentation of Compliance Efforts
Robust documentation is vital for demonstrating compliance, facilitating audits, and ensuring consistency. This includes:
- Policy and Procedure Manuals: Maintaining up-to-date versions of all cybersecurity policies, standards, and operational procedures.
- Risk Assessment Reports: Documenting the results of all risk assessments, including identified assets, threats, vulnerabilities, and risk treatment plans.
- Gap Analysis Reports: Keeping records of initial and subsequent gap analyses, detailing identified deficiencies and remediation efforts.
- Implementation Records: Documenting the deployment and configuration of all security controls, technologies, and system changes.
- Training Records: Maintaining records of all cybersecurity training provided to employees, including attendance and completion rates.
- Incident Response Logs: Documenting all security incidents, from detection to resolution, including actions taken, impact, and lessons learned.
- Audit Trails: Ensuring that system and application logs are properly collected, stored, and available for review.
Comprehensive documentation serves as the official record of your organization’s journey towards and adherence to cybersecurity framework compliance.
Regular Reporting to Management and Board
Effective communication with leadership is crucial to secure continued support and resources for cybersecurity initiatives. Regular reports should provide:
- Compliance Status Updates: A clear overview of the organization’s current compliance posture against the 2026 framework, highlighting areas of strength and areas needing improvement.
- Risk Landscape Overview: Summaries of the most significant cybersecurity risks, their potential impact, and the measures being taken to mitigate them.
- Incident Summaries: Reports on significant security incidents, their resolution, and lessons learned.
- Key Performance Indicators (KPIs) and Metrics: Data-driven insights into the effectiveness of cybersecurity controls and the overall security program.
- Resource Requirements: Justifications for current and future cybersecurity investments, demonstrating their alignment with business objectives and risk reduction goals.
These reports enable informed decision-making at the executive level and underscore the importance of cybersecurity framework compliance to the organization’s overall strategy.
Fostering Internal and External Communication
Communication extends beyond formal reports. It involves creating an open dialogue about cybersecurity:
- Internal Communication: Regularly communicate cybersecurity policies, updates, and best practices to all employees. Encourage a culture where security concerns can be raised without fear.
- Stakeholder Engagement: Engage with relevant internal departments (e.g., legal, HR, operations) to ensure that cybersecurity considerations are integrated into all business functions.
- External Communication (as needed): Be prepared to communicate your compliance efforts to regulators, clients, partners, and the public, especially in the event of a security incident or during due diligence processes.
- Third-Party Vendor Management: Clearly communicate your cybersecurity expectations to third-party vendors and ensure they meet their own compliance obligations.
Transparent communication builds trust, reinforces accountability, and ensures that cybersecurity is a collective responsibility, vital for long-term cybersecurity framework compliance.
Conclusion: Embracing a Proactive Approach to Cybersecurity
The journey to achieving and maintaining cybersecurity framework compliance with the 2026 National Cybersecurity Framework is a significant undertaking, but it is an investment that pays dividends in resilience, trust, and business continuity. The digital world will only become more complex and perilous, making a proactive and structured approach to cybersecurity not just beneficial, but absolutely essential for survival and success.
By following these five practical steps – comprehensive risk assessment and gap analysis, developing a tailored implementation plan, implementing robust controls, continuous monitoring and improvement, and thorough documentation and communication – organizations can systematically build and strengthen their cyber defenses. This isn’t merely about ticking boxes; it’s about embedding cybersecurity into the very fabric of your operations and culture.
Remember that cybersecurity framework compliance is an ongoing process, not a destination. The threat landscape is a moving target, and your organization’s security posture must adapt continuously. Embrace the principles of the 2026 framework as a living guide, allowing it to inform your strategies and drive your continuous efforts to protect your most valuable digital assets. By doing so, you will not only meet regulatory expectations but also foster an environment of security and trust that will empower your organization to thrive in the years to come.
Start your journey today. Assess, plan, implement, monitor, and communicate. Your organization’s future security depends on it.
Author