Cybersecurity Policy 2026: Federal Guidelines for Small Businesses
Cybersecurity Policy 2026: How New Federal Guidelines Affect Small Businesses (PRACTICAL SOLUTIONS)
The digital landscape is constantly evolving, and with it, the threats that lurk within. For small businesses, navigating this complex environment can be particularly challenging. The upcoming Cybersecurity Policy 2026 represents a significant shift in federal guidelines, promising to reshape how organizations, especially small business cybersecurity, approach their digital defenses. This comprehensive guide will delve into the intricacies of these new regulations, break down their implications, and, most importantly, provide practical, actionable solutions to ensure your business not only complies but thrives in this new era of enhanced cybersecurity.
Understanding the Cybersecurity Policy 2026 is not just about avoiding penalties; it’s about safeguarding your assets, protecting your customers’ trust, and maintaining operational continuity. Cyberattacks disproportionately affect small businesses, often leading to severe financial losses and reputational damage. With the new federal guidelines on the horizon, proactive preparation is no longer an option but a necessity. Let’s explore what these changes entail and how your small business cybersecurity strategy can adapt effectively.
The federal government’s increasing focus on cybersecurity reflects a growing recognition of the interconnectedness of our digital infrastructure. Weak links, regardless of size, can compromise larger systems. Therefore, the Cybersecurity Policy 2026 aims to establish a baseline of security measures that all businesses, including small enterprises, must adhere to. This article will serve as your roadmap to understanding these critical changes and implementing robust small business cybersecurity practices.
The Evolving Landscape of Small Business Cybersecurity and the Need for New Policies
Before diving into the specifics of the Cybersecurity Policy 2026, it’s crucial to understand why such comprehensive federal guidelines are becoming imperative. Small businesses are often perceived as less secure targets than large corporations, making them attractive to cybercriminals. They frequently lack the dedicated IT staff, budgets, and advanced security infrastructure of their larger counterparts. This vulnerability makes robust small business cybersecurity a critical national concern.
Recent years have seen an alarming rise in cyberattacks targeting small and medium-sized enterprises (SMEs). Phishing scams, ransomware attacks, and data breaches are common occurrences, leading to significant disruptions. The average cost of a data breach for small businesses can be devastating, often leading to bankruptcy. The new federal guidelines under Cybersecurity Policy 2026 are designed to mitigate these risks by mandating specific security protocols, thereby raising the overall bar for small business cybersecurity.
These policies are not designed to burden small businesses but to empower them with a framework for protection. By standardizing certain security practices, the government aims to create a more resilient digital ecosystem. This proactive approach will help small businesses defend against increasingly sophisticated threats and ensure they can continue to contribute to the economy without undue risk from cyber adversaries. Effective small business cybersecurity is no longer just good practice; it’s becoming a regulatory requirement.
Key Components of Cybersecurity Policy 2026 Affecting Small Businesses
While the full text of the Cybersecurity Policy 2026 is extensive, several core components are particularly relevant to small businesses. Understanding these areas is the first step toward achieving compliance and strengthening your small business cybersecurity posture. We anticipate that the new guidelines will focus on:
Mandatory Risk Assessments and Management
One of the foundational elements of the Cybersecurity Policy 2026 will likely be the requirement for regular, thorough risk assessments. Small businesses will need to identify, analyze, and evaluate potential cyber threats and vulnerabilities within their systems. This isn’t a one-time task; it’s an ongoing process. Practical solutions include:
- Conducting Annual Risk Assessments: Utilize frameworks like NIST (National Institute of Standards and Technology) Cybersecurity Framework‘s Identify function to pinpoint assets, threats, and vulnerabilities.
- Implementing Risk Management Plans: Develop strategies to mitigate identified risks, prioritizing those with the highest potential impact.
- Regular Review and Updates: As your business evolves and new threats emerge, your risk assessment and management plans must be updated accordingly.
Enhanced Data Protection and Privacy Standards
Data is the new oil, and its protection is paramount. The Cybersecurity Policy 2026 is expected to introduce stricter rules around how small businesses collect, store, process, and transmit sensitive data, including customer information, financial records, and intellectual property. This will directly impact small business cybersecurity practices.
- Data Encryption: Mandating encryption for data at rest and in transit, especially for sensitive information. Implement strong encryption protocols for all data storage and communication channels.
- Access Controls: Implementing stricter access controls based on the principle of least privilege, ensuring employees only have access to the data necessary for their roles.
- Data Minimization: Adopting practices to collect and retain only the data that is absolutely necessary, reducing the potential impact of a breach.
- Incident Response Planning: Developing and regularly testing a comprehensive incident response plan to quickly detect, contain, and recover from data breaches.
Mandatory Cybersecurity Training and Awareness
Human error remains one of the weakest links in any cybersecurity chain. The Cybersecurity Policy 2026 will likely emphasize the importance of continuous employee training and awareness programs. This is a crucial aspect of small business cybersecurity.
- Regular Training Sessions: Conduct mandatory cybersecurity training for all employees at least annually, covering topics like phishing awareness, strong password practices, and identifying suspicious activity.
- Simulated Phishing Attacks: Periodically conduct simulated phishing campaigns to test employee vigilance and reinforce training.
- Clear Policy Communication: Establish and clearly communicate internal cybersecurity policies and procedures to all staff.
Vendor and Supply Chain Security Requirements
Small businesses often rely on third-party vendors and cloud services. The Cybersecurity Policy 2026 will extend its reach to ensure that these external dependencies do not introduce new vulnerabilities. Your small business cybersecurity extends beyond your own four walls.
- Vendor Risk Assessments: Evaluate the cybersecurity posture of all third-party vendors and service providers.
- Contractual Obligations: Include cybersecurity clauses in all vendor contracts, outlining their responsibilities and your expectations for data protection.
- Supply Chain Mapping: Understand your supply chain and identify potential points of vulnerability.
Incident Reporting Requirements
Timely and accurate reporting of cyber incidents is vital for national cybersecurity efforts. The Cybersecurity Policy 2026 will likely mandate specific timelines and formats for reporting breaches and other significant cybersecurity events. This will be a new, critical aspect of small business cybersecurity.
- Defined Reporting Procedures: Establish clear internal procedures for identifying and reporting cybersecurity incidents.
- Designated Reporting Contacts: Identify the relevant federal agencies or bodies to whom incidents must be reported.
Practical Solutions for Small Business Cybersecurity Compliance
Now that we’ve outlined the anticipated components of the Cybersecurity Policy 2026, let’s explore practical, actionable solutions your small business can implement today to prepare for and comply with these new federal guidelines. Proactive measures are key to successful small business cybersecurity.
1. Implement a Comprehensive Cybersecurity Framework
Adopting a recognized cybersecurity framework provides a structured approach to managing your security risks. The NIST Cybersecurity Framework is an excellent, flexible option that can be tailored to businesses of all sizes.
- Identify: Understand your assets, systems, data, and capabilities.
- Protect: Develop and implement appropriate safeguards to ensure the delivery of critical services.
- Detect: Develop and implement appropriate activities to identify the occurrence of a cybersecurity event.
- Respond: Develop and implement appropriate activities to take action regarding a detected cybersecurity incident.
- Recover: Develop and implement appropriate activities to maintain plans for resilience and to restore any capabilities or services that were impaired due to a cybersecurity incident.
By systematically working through these functions, you can build a robust small business cybersecurity program that aligns with federal expectations.
2. Fortify Your Network and Systems
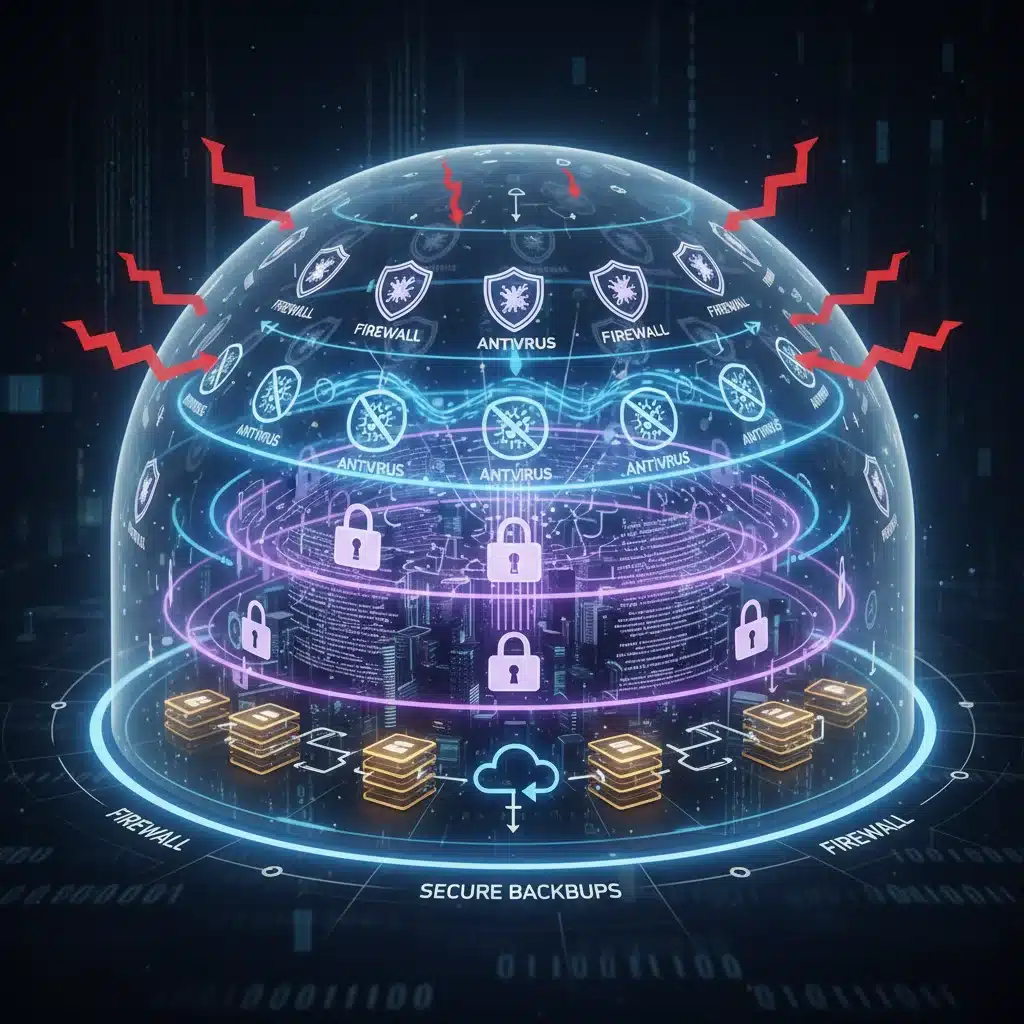
Basic, yet critical, network and system security measures form the backbone of your small business cybersecurity defenses.
- Firewall Protection: Ensure you have a properly configured firewall to control incoming and outgoing network traffic.
- Antivirus and Anti-Malware Software: Install and regularly update reputable antivirus and anti-malware solutions on all devices.
- Patch Management: Implement a rigorous patch management process to ensure all software, operating systems, and applications are up-to-date with the latest security patches.
- Secure Wi-Fi Networks: Use strong encryption (WPA3 where available) and unique, complex passwords for your Wi-Fi networks. Isolate guest networks from your main business network.
- Intrusion Detection/Prevention Systems (IDPS): Consider implementing IDPS to monitor network traffic for malicious activity and automatically block threats.
3. Strengthen Access Management
Controlling who has access to what information is fundamental to small business cybersecurity.
- Strong Password Policies: Enforce the use of strong, unique passwords that are regularly changed. Consider password managers to help employees.
- Multi-Factor Authentication (MFA): Implement MFA for all accounts, especially for access to sensitive data, cloud services, and network logins. This adds a crucial layer of security.
- Principle of Least Privilege: Grant employees only the minimum level of access required to perform their job functions. Regularly review and revoke unnecessary access.
- User Account Management: Have clear procedures for creating, modifying, and deleting user accounts, especially during employee onboarding and offboarding.
4. Prioritize Data Backup and Recovery
Even with the best defenses, breaches can occur. A robust backup and recovery strategy is vital for business continuity and a key component of effective small business cybersecurity.
- Regular Backups: Implement automated, regular backups of all critical data.
- Offsite and Cloud Backups: Store backups in multiple locations, including offsite or secure cloud storage, to protect against physical disasters.
- Test Backups: Regularly test your backup restoration process to ensure data can be recovered successfully and efficiently.
- Immutable Backups: Consider immutable backups that cannot be altered or deleted, providing a strong defense against ransomware.
5. Cultivate a Culture of Cybersecurity Awareness
Your employees are your first line of defense. Investing in their knowledge and vigilance is paramount for small business cybersecurity.
- Ongoing Training: Beyond initial training, provide regular refreshers and updates on new threats and best practices.
- Simulated Attacks: Use phishing simulations to train employees to identify and report suspicious emails.
- Clear Communication: Regularly communicate cybersecurity news, tips, and policy updates to your team.
- Reward Good Practices: Acknowledge and reinforce employees who demonstrate good cybersecurity habits.
6. Secure Your Cloud and Third-Party Services
Many small businesses rely heavily on cloud services. Ensuring these are secure is a critical part of your small business cybersecurity strategy.
- Due Diligence: Before engaging a cloud provider or third-party vendor, thoroughly vet their security practices and certifications.
- Service Level Agreements (SLAs): Review SLAs to understand their security responsibilities and your own.
- Configuration Best Practices: Properly configure cloud services, paying close attention to access controls, data encryption, and logging. Misconfigurations are a common cause of cloud breaches.
- Regular Audits: Periodically audit your cloud configurations and third-party access to ensure continued compliance and security.
7. Develop and Test an Incident Response Plan
No matter how prepared you are, a cyber incident is always a possibility. Having a well-defined and tested incident response plan is crucial for minimizing damage and ensuring business continuity for small business cybersecurity.
- Identification: How will you detect an incident?
- Containment: How will you limit the damage?
- Eradication: How will you remove the threat?
- Recovery: How will you restore systems and data?
- Post-Incident Analysis: What lessons can be learned to prevent future incidents?
Regularly drill your incident response plan with your team to ensure everyone knows their roles and responsibilities. This preparedness is a cornerstone of effective small business cybersecurity.
Leveraging Technology for Enhanced Small Business Cybersecurity
While policies and training are vital, technology plays a crucial role in implementing effective small business cybersecurity. Consider integrating these solutions:
- Endpoint Detection and Response (EDR): EDR solutions provide advanced threat detection and response capabilities for endpoints (laptops, desktops, servers), going beyond traditional antivirus.
- Security Information and Event Management (SIEM): For larger small businesses, SIEM solutions can aggregate and analyze security logs from various sources, providing a centralized view of security events and aiding in threat detection.
- Managed Security Service Providers (MSSPs): If your business lacks in-house cybersecurity expertise, consider partnering with an MSSP. They can provide 24/7 monitoring, incident response, and compliance assistance, significantly enhancing your small business cybersecurity posture.
- Data Loss Prevention (DLP): DLP solutions help prevent sensitive data from leaving your organization’s control, whether intentionally or accidentally.
- Vulnerability Scanners: Regularly scan your network and applications for known vulnerabilities that attackers could exploit.
The Financial Aspect: Budgeting for Cybersecurity Policy 2026 Compliance
Many small businesses worry about the cost of compliance. While there will be an investment, viewing cybersecurity as a cost center rather than a strategic investment is a short-sighted approach. The cost of a breach far outweighs the cost of prevention. When budgeting for small business cybersecurity, consider:
- Software and Hardware: Firewalls, antivirus, EDR, backup solutions, and potentially hardware upgrades.
- Training: Employee awareness programs, external training for key personnel.
- Consulting: Engaging cybersecurity experts for risk assessments, penetration testing, or developing incident response plans.
- Insurance: Cyber insurance can provide a safety net in the event of a breach, covering costs like legal fees, notification expenses, and business interruption.
Explore government grants or programs that might be available to assist small businesses with cybersecurity initiatives. Being prepared for the Cybersecurity Policy 2026 means allocating appropriate resources to your small business cybersecurity strategy.
Staying Ahead: Continuous Monitoring and Adaptation
The digital threat landscape is dynamic. What is secure today might be vulnerable tomorrow. Therefore, compliance with Cybersecurity Policy 2026, and effective small business cybersecurity in general, requires continuous monitoring and adaptation.
- Regular Audits and Reviews: Periodically review your security controls, policies, and procedures to ensure they remain effective and aligned with the latest threats and regulations.
- Threat Intelligence: Stay informed about emerging cyber threats and vulnerabilities relevant to your industry.
- Feedback Loops: Encourage employees to report suspicious activities and use this feedback to improve your security posture.
- Adaptability: Be prepared to adjust your small business cybersecurity strategies as new technologies emerge and regulations evolve.
The Cybersecurity Policy 2026 is not a static document; it will likely be updated and refined over time. Your commitment to continuous improvement in small business cybersecurity will be crucial for long-term success.
Conclusion: Embracing a Secure Future for Your Small Business
The Cybersecurity Policy 2026 is set to usher in a new era of federal guidelines that will significantly impact small businesses. While the prospect of new regulations can seem daunting, viewing these changes as an opportunity to strengthen your small business cybersecurity posture is essential. By understanding the key components of the policy and implementing practical solutions, your business can not only achieve compliance but also build a resilient defense against an ever-growing array of cyber threats.
Proactive risk assessments, robust data protection, continuous employee training, secure vendor management, and a well-tested incident response plan are not just regulatory requirements; they are fundamental pillars of modern business operations. Investing in small business cybersecurity is an investment in your business’s future, safeguarding its reputation, financial stability, and ability to serve its customers effectively.
Start preparing today. Assess your current small business cybersecurity defenses, identify gaps, and begin implementing the solutions outlined in this guide. By taking these steps, your small business can confidently navigate the Cybersecurity Policy 2026 and emerge stronger, more secure, and ready for the challenges of the digital age.
Author